Data privacy law continues to reshape how UK businesses approach digital marketing. With the post-Brexit evolution of the UK GDPR and the Information Commissioner's Office (ICO) increasing its enforcement activity, 2026 is not the year to be complacent about compliance. Whether you run a small independent business in Halifax or a multi-site operation across Yorkshire, understanding what GDPR-compliant digital marketing looks like in practice is no longer optional — it is a legal and commercial necessity. At STEPS Solutions, we work with UK businesses every day to align their digital marketing strategies with both best-practice privacy standards and strong commercial performance. This guide gives you a clear, actionable overview of everything you need to know.
What Is UK GDPR and How Does It Differ From EU GDPR in 2026?
Since Brexit, the United Kingdom operates under its own version of data protection law, commonly referred to as UK GDPR, which sits alongside the Data Protection Act 2018. While it closely mirrors the EU GDPR in structure and principle, the UK retains its own regulatory framework governed by the Information Commissioner's Office (ICO) rather than EU supervisory authorities.
In 2026, UK businesses must be aware of several key developments:
- The Data (Use and Access) Act 2025 has introduced updates to how data intermediaries and smart data schemes operate, with knock-on implications for digital marketing data flows.
- Transfers of personal data between the UK and EU remain permissible under existing adequacy decisions, but businesses operating in both markets must maintain compliance with both frameworks.
- The ICO has sharpened its focus on consent mechanisms, cookie compliance, and direct marketing practices, issuing fines and reprimands at an increasing rate.
For the purposes of GDPR-compliant digital marketing, the core principles — lawfulness, fairness, transparency, purpose limitation, data minimisation, accuracy, storage limitation, and accountability — remain unchanged and fully enforceable.
The Six Lawful Bases for Digital Marketing: Which One Applies to You?
One of the most common areas of confusion for UK businesses is identifying the correct lawful basis for processing personal data in a marketing context. UK GDPR sets out six lawful bases, but digital marketing typically relies on two:
1. Consent
Consent must be freely given, specific, informed, and unambiguous. In digital marketing, this means:
- Pre-ticked boxes are not valid — users must take a positive action.
- Consent must be granular — separate opt-ins for email marketing, SMS, and third-party sharing.
- You must keep records of when and how consent was obtained.
- Withdrawing consent must be as easy as giving it.
2. Legitimate Interests
Legitimate interests can be used as a basis for some marketing activities, but only after completing a three-part Legitimate Interests Assessment (LIA): purpose test, necessity test, and balancing test. This basis is more appropriate for B2B marketing and existing customer communications than for cold outreach to consumers.
"The ICO expects businesses to be able to demonstrate compliance, not just claim it. If you cannot show how and when consent was collected, you do not have valid consent." — ICO Guidance on Direct Marketing, 2024
Cookies, Tracking, and Consent Management in 2026
Cookie compliance remains one of the highest-risk areas for digital marketers. The Privacy and Electronic Communications Regulations (PECR) work alongside UK GDPR to govern the use of cookies and similar tracking technologies. In 2026, the ICO's enforcement focus has expanded beyond large platforms to include SMEs across sectors.
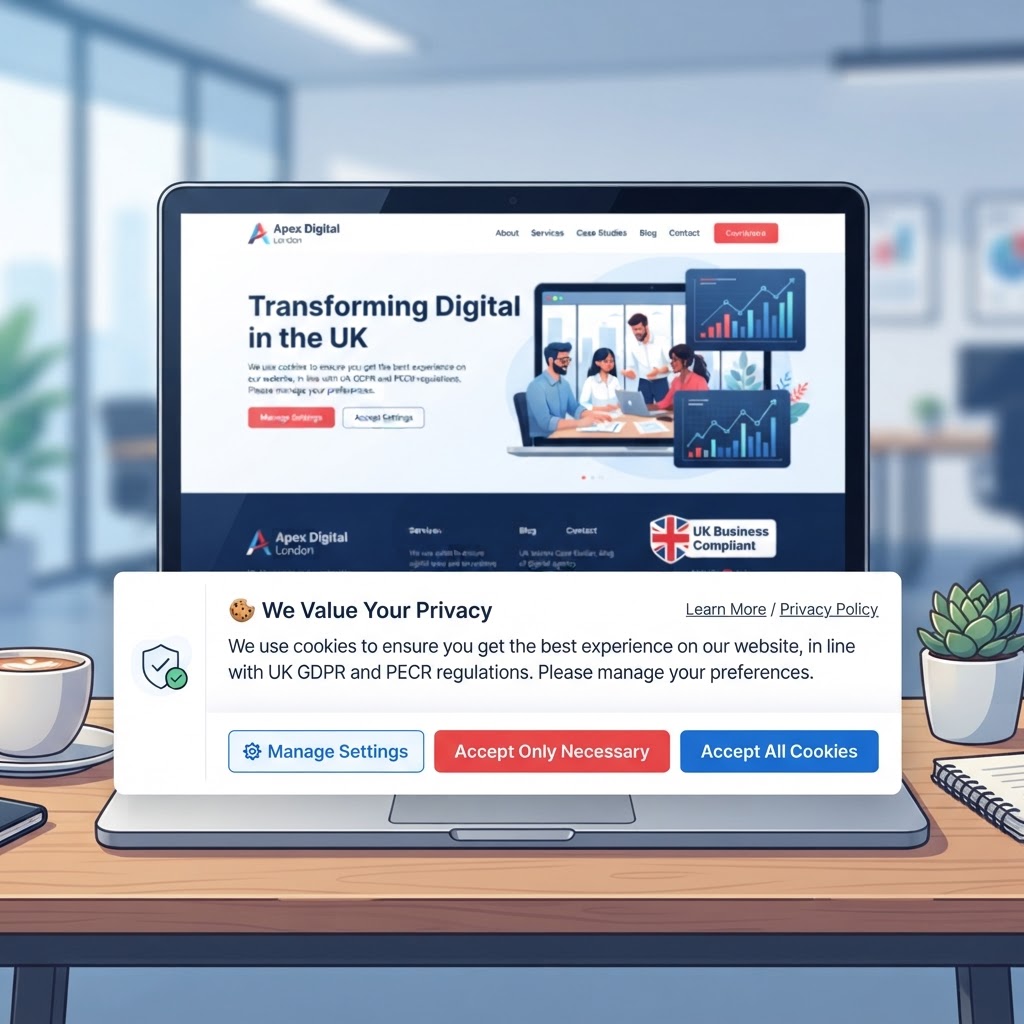
For a cookie consent solution to be compliant, your website must:
- Present a cookie consent banner before any non-essential cookies are loaded.
- Give users a genuine, equal-prominence option to accept or reject non-essential cookies.
- Avoid dark patterns — such as making "accept all" easier to click than "reject all".
- Allow users to change their preferences at any time via an accessible cookie settings panel.
- Document consent records and keep your cookie policy up to date as your tech stack evolves.
At STEPS Solutions in Halifax, we audit and implement compliant Consent Management Platforms (CMPs) as part of our website development service, ensuring that analytics, advertising pixels, and third-party scripts only fire when legally permitted to do so.
Email Marketing and GDPR: What UK Businesses Must Get Right
Email marketing remains one of the highest-ROI digital channels, but it is also one of the most tightly regulated. The combination of UK GDPR and PECR means that sending unsolicited marketing emails to individuals without a valid basis is unlawful.
Consumer Email Marketing (B2C)
For individual consumers, you must have prior opt-in consent to send marketing emails. The only exception is the soft opt-in rule, which allows you to email existing customers about similar products or services — provided you gave them a clear opportunity to opt out at the point of data collection and in every subsequent message.
Business Email Marketing (B2B)
PECR treats emails sent to corporate addresses (e.g., info@company.co.uk) differently from personal addresses. Legitimate interests may apply, but you must still respect opt-out requests immediately and ensure your targeting is relevant and proportionate.
Best practice for all email marketing in 2026 includes maintaining a clean, permission-based mailing list, including a visible unsubscribe link in every message, and honouring opt-outs within ten working days (though best practice is immediate suppression).
Social Media Advertising, Remarketing, and Data Minimisation
Paid social advertising — whether on Meta, LinkedIn, or TikTok — involves processing personal data through audience targeting, custom audiences, and pixel-based remarketing. UK businesses using these tools must ensure their privacy notices accurately disclose this processing and that website visitors have consented to the relevant tracking cookies before any remarketing pixels fire.
Key compliance considerations for social media marketing include:
- Only uploading customer list data to ad platforms where you have a valid lawful basis for that processing.
- Ensuring your data processing agreements (DPAs) with platforms like Meta are in place and up to date.
- Applying data minimisation — only collect and share the data fields genuinely necessary for the campaign objective.
- Reviewing your privacy policy to include clear references to social media advertising and third-party data sharing.
Building a GDPR-Compliant Digital Marketing Strategy: Practical Steps
Compliance does not have to mean limiting your marketing effectiveness. The businesses that thrive are those that build trust through transparency and use first-party data strategically. Here is how to approach this in 2026:
- Conduct a data audit: Map every touchpoint where personal data enters your marketing systems — web forms, CRM imports, ad platform integrations, and email lists.
- Review your consent flows: Test your website as a new visitor. Does the consent journey meet ICO standards? Is your CMP functioning correctly?
- Update your privacy notice: Ensure it is current, plain-English, and covers all processing activities including analytics and advertising.
- Train your team: Everyone involved in marketing decisions should understand the basics of UK GDPR as it applies to their role.
- Work with compliant suppliers: Ensure any agency, CRM provider, or martech platform you use has signed a Data Processing Agreement with you.
The team at STEPS Solutions, based in Halifax, West Yorkshire, helps businesses across Yorkshire and the wider UK integrate compliance into their digital marketing strategy from the ground up — without sacrificing performance or growth.
Key Takeaways
- UK GDPR is the governing data protection framework for UK businesses in 2026, enforced by the ICO.
- Valid consent for digital marketing must be freely given, specific, informed, and unambiguous — pre-ticked boxes are not compliant.
- Cookie banners must present accept and reject options with equal prominence, and non-essential cookies must not load before consent is given.
- Email marketing to consumers requires prior opt-in under PECR, with the soft opt-in rule as the only limited exception.
- Social media advertising and remarketing require valid cookie consent and up-to-date privacy notices.
- First-party data and transparent data practices are both a legal requirement and a competitive advantage in 2026.
- STEPS Solutions in Halifax helps Yorkshire businesses build compliant, high-performing digital marketing strategies.
Frequently Asked Questions
Does UK GDPR still apply to digital marketing after Brexit?
Yes. UK GDPR, which closely mirrors the EU GDPR, continues to apply to all UK businesses processing personal data for marketing purposes. It is enforced by the Information Commissioner's Office (ICO). Businesses operating in both the UK and EU must comply with both frameworks independently.
What is the lawful basis for sending marketing emails in the UK?
For consumer email marketing (B2C), you generally need prior opt-in consent under PECR. The soft opt-in rule allows existing customers to be emailed about similar products or services without fresh consent, provided they were given an opt-out opportunity originally. For B2B emails to corporate addresses, legitimate interests may apply, but you must still respect opt-out requests.
Are cookie banners legally required on UK websites?
Yes. Under the Privacy and Electronic Communications Regulations (PECR), UK websites must obtain informed consent before placing non-essential cookies on a user's device. Cookie consent banners must offer a genuine choice — accept and reject options must be presented with equal prominence. Loading analytics or advertising cookies before consent is obtained is a breach of PECR.
Can I use Meta custom audiences and still be GDPR compliant?
Yes, but only if you have a valid lawful basis to process the personal data you are uploading (such as an email list built on consent), you have disclosed this use in your privacy notice, and you have a current Data Processing Agreement in place with Meta. You must also ensure that Meta's advertising pixel only fires on your website after a visitor has given valid cookie consent.
What are the penalties for non-compliant digital marketing in the UK?
The ICO can issue fines of up to £17.5 million or 4% of global annual turnover (whichever is higher) for serious UK GDPR breaches. For PECR violations relating to cookies and direct marketing, fines of up to £500,000 can be issued. Beyond financial penalties, the ICO can issue enforcement notices, reprimands, and in extreme cases, orders to cease processing data — all of which can cause significant reputational damage.